William J. Lynn III Quotes
A few young guys with a case of Red Bull can be a serious security threat.
He was referring to the potential of computer enthusiasts hacking into the Internet grid and bringing it or significant parts of it down. Unlike other forms of attacks on national security resources, cyber security danger often comes from people who do damage just for the challenge of doing it—in addition to the political or military enemies. Red Bull is a high alcohol content beer.
William J. Lynn III, Deputy Secreatry of Defense, Interview, The Charlie Rose Show, October 18, 2010
Sourced by: Eigen's Political and Historical Quotations

In addition to the hackers who break into websites for monetary gain, or spying for companies or governments, there are many why just love the challenge of hacking into computers and websites that authorities claim is secure. The reality is that there is no way to absolutely sure a computer or its contents as long as it is connected to the Internet. Those computers and sites that have nothing to hide and do not present a challenge to hackers of this type rarely have problems from them; their vulnerability is to the other hacker who can utilize their computer slo hack still others of paralyze their computer to extract a ransom for functionality. The analogy of the hackers to the barbarian hordes sacking Ancient Rome and the Mongolian hordes sacking Europe is one that many appreciated,

Many computer experts and security operatives view this kind of advice and strategy as counter-productive as there are some computer security extremists who so harden computer systems and networks that they function poorly and cause really harmful operational problems. The classic case was the FBI agent in Minnesota who before 9-11 had information that Muslims foreigners were taking flying lessons. She wanted to get the information to the national security FBI people, but she was not allowed to send the information by e-mail. Instead she had to use a "secure" system that was much slower and could not be viewed by the people who might have been able to connect the dots and do something about it. The FBI has now a better balance between functionality and security, but it is a good example of how "security fanaticism" can make us less safe.


A number of the hacking incidents that occurred in 2016 were done by foreign governments. This was a subtle form of threatening those nations who had been doing the hacking of American public and private entities. Without making any overt threat to retaliate, he was reminding would be future hackers to desist less the U. S. decide to retaliate in kind with greater capacity and more sophisticated techniques.

There is a constant race between the developers of hacking and cyberattack software and the developers of security and protective software.


Actually, Rothkopf's description of the knowledge of national security officials about nuclear bombs is somewhat exaggerated. When there was a schism between the scientists who had developed the atom bomb and the military and national security people. The later thought that they knew the field well enough, but the nuclear testing at Bikini and other efforts were bungled strategically and operationally. However, there was proportionately much more knowledge then than there is now. This was in spite of the fact that almost everything nuclear was top secret and unavailable to many people to develop the knowledge, while almost everything about cyber security was available and in the public domain. So Rothkopf's basic point was correct, though his history was somewhat flawed.
A few weeks before, the computers of the Democratic National Committee were hacked and thousands of private and confidential e-mails were made public. The security experts claimed that the hackers came from Russia.

Arguing for a standing army:


In the digital technology era, the personal computer enabled tens of thousands of young people to become highly skillful at computer technology. Some of them tended to disagree with the government or protest areas of society using the technology to learn information of to communicate their ideas to the world. The government authorities did not have many people who were in the same technological class and very frequently authorities with virtually unlimited resources to protect government secrets or government facilities were embarrassed by being outsmarted by usually young people with little or no resources. When the authorities were embarrassed, they tended to arrest the “hacktivists” and charge them with very serious crimes—far greater or trumped up from no crime at all, in order to punish the hacktivists and discourage others.
In the early 21st century hackers who committed fraud and stole much money were not considered as serious as hackers who would have a political (anti-government) message display on the government’s own website. The latter were considered much more of a threat than the former although the only “damage” the former did was inconvenience and embarassment to government officials.

He was the Chairman of the Senate Judiciary Committee. The NSA had hacked into the servers of these firms and others that were located out of the country. (They would need to have a warrant if inside the country.) The companies had never known it until Edward Snowden made this practice public. The result was, the public was learning that there was no privacy in any of their e-mail, social media activity, exchange of photos or videos or anything else. The companies feared that this would then harm their business, and that the techniques NSA used to hack there servers would then be discovered and used by others to steal identities, credit cards and do such other damage to customers. Even if the particular hacking methods were not leaked to the bad guys, they, knowing that the servers were vulnerable, would be encouraged to work to figure it out.

Describing the increasing trend of young computer hackers who generally had hacked just for the challenge getting involved in hacking with a political and ideological causes—sometimes even working for governments.
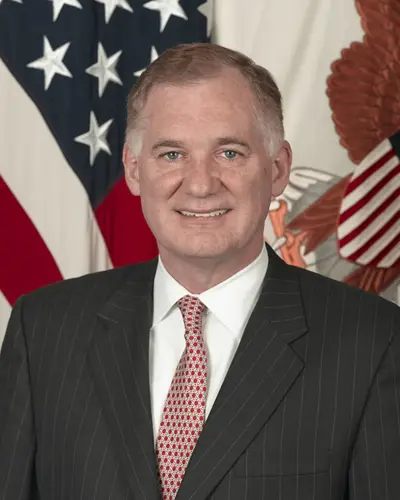
William J. Lynn III is a former United States Deputy Secretary of Defense. Before that he was Under Secretary of Defense (Comptroller) and a lobbyist for Raytheon.
